

In the 1980s, downloading a 150 KB file from a bulletin board system was not exactly a fast operation. With a 300-baud modem, you could spend well over an hour waiting for a file to arrive. And while your computer was connected, nobody in the house could use the telephone line.
For hackers and phone phreaks of the era, however, those painfully slow downloads could contain something far more valuable than software.
They could contain the Legion of Doom Technical Journal.
Today, the name sounds like something taken directly from a comic book. In fact, that’s exactly where it came from. But the real Legion of Doom was not a fictional supervillain organization. It was one of the most influential hacker groups of the 1980s and early 1990s—a loose collection of technically skilled hackers who explored telephone systems, computer networks, X.25 infrastructure, Unix systems, and other emerging technologies.
They also documented what they learned.
That combination of technical curiosity, underground publishing, experimentation, and a controversial hacker ethic helped shape the culture that would eventually become modern information security.
From Super Friends to the Legion of Doom

The story begins around 1984, when a Texas hacker using the alias Lex Luthor founded the Legion of Doom after a split with another underground group, the Knights of Shadow.
The name was borrowed from the villains of the animated Challenge of the Super Friends. In the cartoon, Lex Luthor led a team of comic-book villains from an enormous headquarters shaped like a giant helmet.
The real Legion of Doom obviously didn’t have anything quite that impressive.
Their headquarters were computers, modems, telephone lines and bulletin board systems.
The contrast was almost perfect: a group of teenagers and young adults using ordinary home computers to explore some of the most complicated communications infrastructure in the United States.
And unlike the cartoon villains, their main weapon wasn’t brute force.
It was knowledge.
Before Hackers, There Were Phone Phreaks
To understand the Legion of Doom, you first need to understand phone phreaking.
Long before smartphones and the modern internet, the telephone network itself was a gigantic technological playground.
Phone phreaks discovered that parts of the network relied on audible tones and signaling systems. By generating or manipulating the right signals, it was sometimes possible to make the telephone system behave in unexpected ways.
One of the most famous tools was the blue box, which generated signaling tones used by telephone switching systems.
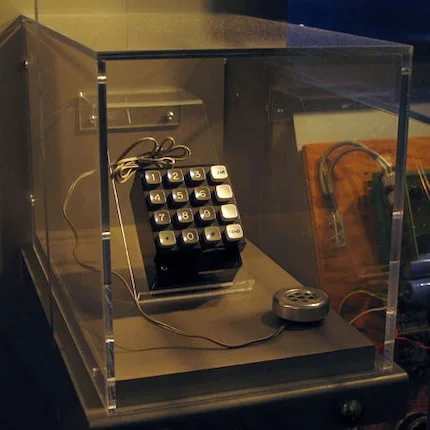
The legendary 2600 Hz tone became deeply associated with phone phreaking, and figures such as John Draper—better known as Captain Crunch—helped turn phone phreaking into a cultural phenomenon.
There were also red boxes, which attempted to simulate coin tones on payphones, along with increasingly sophisticated forms of social engineering.
Instead of exploiting software, social engineering exploited something much older:
human beings.
A hacker could call a telephone company employee, pretend to be a technician, establish credibility and convince the employee to reveal information that should never have been disclosed.
The Legion of Doom inherited this culture but pushed it toward something more systematic.
They weren’t interested only in making free phone calls.
They wanted to understand how the systems worked.
Legion of Doom Was About Knowledge
This is one of the reasons LOD became so influential.
Members explored telephone company systems, computer networks and other infrastructure, then shared technical information with selected members of the underground.
The group became associated with an unusually strong emphasis on technical knowledge and documentation.
That eventually produced one of its most important creations:
the Legion of Doom Technical Journal.
The publication became a major source of technical information within the hacker underground and was deliberately named as a parody of the much more respectable AT&T Technical Journal. Bruce Sterling later described how the LOD journal began circulating widely through underground bulletin boards.
The distinction is important, though.
The idea that LOD simply followed a clean rule of “hack but never cause damage” is too simplistic. Members accessed systems without authorization, and some were accused or convicted of damaging or manipulating telephone and computer systems. The group itself cultivated an image of hackers as explorers rather than vandals, but the legal reality was considerably messier.
Erik Bloodaxe: One of LOD’s Most Famous Hackers
Among the best-known members was Erik Bloodaxe, the alias of Chris Goggans.
Goggans became one of the prominent technical figures associated with LOD and later became an information-security professional.
His reputation was built around a deep understanding of computer networks and telecommunications systems—exactly the kind of knowledge that made the Legion of Doom so intimidating to companies and law enforcement agencies.
This was the era when corporate networks were becoming interconnected but security practices were still primitive by modern standards.
A technically skilled person who understood telephone infrastructure, remote-access systems, Unix machines and networking protocols could sometimes move through environments that had never been designed with hostile users in mind.
The modern cybersecurity industry would eventually turn that exact skill set into a profession.
The Legion of Doom Technical Journal
In 1987, the Legion of Doom Technical Journal became one of the group’s defining publications.
Only a small number of official issues were produced, but their influence was much larger than their publication count suggests. Historical sources identify three major issues, with the project eventually disrupted by the wave of law-enforcement investigations against members of the underground.
The material covered the kind of subjects that were almost impossible for outsiders to understand at the time.
Telephone switching.
Digital multiplexing.
Computer networking.
Unix.
Mainframes.
Remote-access systems.
X.25 networks.
Telecommunications infrastructure.
The documents were not polished corporate security reports. They were underground technical papers, often written in a mixture of detailed technical explanation, hacker slang and humor.
But they had something extremely valuable:
practical knowledge.
The Technical Journal helped demonstrate that hackers could be researchers, writers and teachers—not simply people breaking into computers.
You can still explore archived LOD material today through online text archives. The original files are a fascinating snapshot of what technical knowledge looked like inside the 1980s hacker underground.
The Hacker Manifesto
If the Technical Journal represented the technical side of the culture, The Mentor represented its philosophical side.
The Mentor was the alias of Loyd Blankenship, a prominent hacker who became associated with the Legion of Doom.
In January 1986, after being arrested during a Secret Service investigation in Austin, Blankenship wrote what became one of the most famous texts in hacker history:
“The Conscience of a Hacker.”
It later became widely known as the Hacker Manifesto.
The text was short, but its message was powerful.
Blankenship argued that hackers were motivated by curiosity and the desire to understand systems, while society often interpreted that curiosity as criminality.
The manifesto became one of the defining texts of hacker culture and was subsequently reprinted by Phrack.
The important thing is that it wasn’t a technical manual.
It was a statement of identity.
The hacker was not necessarily supposed to be a thief or vandal. In Blankenship’s vision, the hacker was someone who wanted to explore systems that others considered inaccessible.
That distinction would influence hacker culture for decades.
The Hacker Manifesto Becomes Part of Pop Culture
“The Conscience of a Hacker” eventually escaped the underground.
It became one of the most recognizable pieces of hacker literature and was later referenced in popular culture, including the 1995 movie Hackers.
Its ideas also became part of the broader debate about hacker ethics.
Today, concepts such as responsible disclosure, security research, penetration testing and bug bounty programs operate within a very different legal framework.
But the underlying question remains surprisingly similar:
Where is the line between curiosity and unauthorized access?
That question was already being debated in the 1980s.
The Steve Jackson Games Raid
The Mentor’s story also became connected to one of the most important legal controversies of the early hacker era.
In March 1990, the U.S. Secret Service raided Steve Jackson Games, a role-playing game publisher in Austin, Texas.
The company had been preparing GURPS Cyberpunk, a sourcebook dealing with a dystopian future involving computers, hacking and technology.
The Secret Service seized computers and electronic material, and investigators reportedly viewed the book as potentially related to computer crime.
The raid became a major civil-liberties controversy.
Steve Jackson Games later sued the government, and the case became an important milestone in the debate over privacy and government searches of electronic data. The Electronic Frontier Foundation identifies the case as a landmark in establishing limits on government power in cyberspace.
The episode also demonstrated something that would become increasingly important during the 1990s:
computer crime investigations could collide with freedom of expression.
LOD’s Private Online World
The Legion of Doom wasn’t simply a collection of individuals who happened to know one another.
The group developed its own underground communication infrastructure.
Its BBS culture was deliberately selective, and access was restricted to people considered sufficiently knowledgeable or trustworthy. Historical accounts describe LOD’s systems as among the early examples of invitation-only hacker BBS communities, with security mechanisms intended to keep outsiders away.
This was the opposite of today’s internet.
There was no Discord.
No Reddit.
No GitHub.
No Stack Overflow.
No instant messaging.
If you wanted to exchange technical information with someone on the other side of the country, you might have needed to dial their BBS through a modem.
And if the group didn’t trust you, you simply didn’t get in.
The result was a small but highly connected technical underground.
Phiber Optik and the Rise of Masters of Deception
Eventually, internal conflicts began to weaken LOD.
One of the most famous figures caught in those tensions was Mark Abene, better known as Phiber Optik.
Born in New York in 1972, Abene became a prominent figure in the hacker scene and was associated with both the Legion of Doom and the later Masters of Deception (MOD).
MOD emerged from New York’s hacker and phreaking scene in the late 1980s.
Its founders included Acid Phreak, Scorpion and HAC, with figures such as Phiber Optik and Corrupt becoming prominent members.
The name itself was partly a joke at LOD’s expense.
Legion of Doom.
Masters of Deception.
Two hacker groups.
Two regions.
Two different cultures.
And plenty of ego.
The “Great Hacker War”
The rivalry between LOD and MOD eventually became known as the Great Hacker War.
The story has become legendary.
Hackers from Texas and New York allegedly attacked each other’s systems, harassed one another, manipulated telephone infrastructure and fought over reputation.
The conflict became one of the most famous stories in hacker history, helped enormously by journalists and books such as Masters of Deception: The Gang That Ruled Cyberspace.
But there’s an important catch.
The “war” itself is disputed.
Later accounts from people who were actually involved have challenged the idea that there was a coordinated cyberwar comparable to the popular version of the story.
At a later HOPE conference, Phiber Optik reportedly described the idea of a “gang war in cyberspace” as largely fabricated or dramatically exaggerated.
There certainly were conflicts, insults, harassment and technical competitions.
But the mythology became larger than the reality.
And that’s a recurring theme in hacker history.
The stories get bigger.
The legends become cleaner.
The historical reality gets messier.
When Hacker Culture Collided With Law Enforcement
Whatever the exact scale of the LOD/MOD rivalry, law enforcement was becoming increasingly interested in the underground.
By the end of the 1980s, authorities were investigating hackers involved in telephone fraud, credit-card theft, unauthorized computer access and other offenses.
Then came Operation Sundevil.
On May 8, 1990, authorities launched a nationwide crackdown involving the Secret Service and other agencies.
Contemporary reporting described raids across numerous U.S. cities. Authorities seized 42 computers and approximately 23,000 floppy disks, along with telephone equipment, BBS material and other records.
The Electronic Frontier Foundation later described Operation Sun Devil as a major law-enforcement campaign against the hacker underground, involving dozens of searches across American cities.
For the underground, the psychological impact was enormous.
BBS operators became nervous.
Hackers became suspicious of one another.
People began disappearing from the scene.
The idea that you could explore computer systems anonymously suddenly seemed much less realistic.
The End of an Era
Operation Sundevil didn’t magically destroy the Legion of Doom overnight.
But it contributed to the collapse of the environment that had allowed groups like LOD to flourish.
Members were investigated, raided or prosecuted.
Others simply stopped participating.
The Technical Journal disappeared.
The underground became more fragmented.
And the golden age of the 1980s hacker BBS culture began to fade.
The old model—small groups of technically gifted teenagers exchanging information through private dial-up systems—was giving way to something much larger.
The internet was coming.
The Hacker Becomes the Security Expert
One of the most fascinating aspects of the Legion of Doom story is what happened to some of its members afterward.
Chris Goggans, the hacker known as Erik Bloodaxe, eventually moved into professional information security.
He worked in network security and consulting and became involved with security assessments and computer-crime investigations. He also went on to participate in professional conferences and security education.
In 2003, Goggans was invited to become a visiting associate professor at the University of Tokyo, where he worked on security education.
That’s one of the great ironies of hacker history.
The same knowledge that once made someone a threat to computer networks could later make that person extremely valuable to the organizations trying to defend those networks.
The hacker and the security professional were not always opposites.
Sometimes they were the same person at different points in their career.
The Legion of Doom’s Legacy
The Legion of Doom disappeared as a major force, but its influence didn’t.
Its members helped popularize the idea that technical knowledge should be documented and shared.
Its Technical Journal became part of the historical record of the early hacking scene.
The Mentor’s manifesto became a foundational text of hacker culture.
The group’s activities helped demonstrate how vulnerable telecommunications and computer systems could be when their designers assumed that users would behave honestly.
And perhaps most importantly, LOD helped establish a culture in which understanding technology at a very deep level was something worth pursuing.
That mentality survives today in penetration testing, vulnerability research, security conferences, CTF competitions and bug bounty programs.
The tools are different.
The legal boundaries are different.
The internet is unimaginably larger.
But the curiosity is remarkably familiar.
From BBSs to Bug Bounties
The transformation from the 1980s hacker underground to today’s cybersecurity industry is almost surreal.
Back then, a teenager with a modem might spend an entire night trying to understand a telephone switch.
Today, a security researcher might spend the same night examining a web application’s source code, reverse-engineering a mobile application or analyzing a vulnerability in a cloud platform.
Then, the reward might have been reputation inside a tiny underground community.
Today, the reward could be a $10,000 bug bounty and a job at a major technology company.
The fundamental motivation, however, can still be the same:
“How does this thing actually work?”
That question is at the heart of security research.
What Happened to the Other Hackers?
The Legion of Doom was never a conventional company with a clean organizational chart, so tracking every member is difficult.
Some became security professionals.
Some were prosecuted.
Some remained active in underground communities.
Others simply disappeared from public view.
The group itself was never a single permanent organization with a fixed membership list. Names and affiliations changed over time, and some people associated with LOD also interacted with other hacker groups.
That’s another reason why many modern descriptions of LOD should be treated cautiously.
The mythology often makes it look like a highly centralized cybercrime organization.
In reality, it was much closer to a loose, evolving network of hackers connected by reputation, friendships, technical interests and underground communication systems.
You Can Still Read the Technical Journals
Here’s the really strange part.
Decades later, much of the material hasn’t disappeared.
Archives of the Legion of Doom Technical Journal remain available online, allowing anyone interested in hacker history to see what these documents actually looked like.
Reading them today is fascinating.
Not because every technique remains relevant—they obviously don’t—but because they reveal how hackers thought about technology before cybersecurity became a mainstream profession.
The terminology is different.
The hardware is ancient.
The networks are primitive by today’s standards.
But the curiosity is immediately recognizable.
Legion of Doom: More Than a Hacker Gang
It would be easy to remember the Legion of Doom simply as a gang of teenage hackers who broke into telephone companies.
That would miss the bigger story.
LOD existed during a transitional moment when computers were moving from isolated machines toward interconnected systems.
The group explored that new world before society had developed the vocabulary to describe what was happening.
They experimented with systems that were never designed to resist hostile users.
They documented their discoveries.
They argued about ethics.
They fought with rivals.
They attracted the attention of law enforcement.
And eventually, some of the people who had once been considered dangerous hackers became security professionals.
That’s why the Legion of Doom remains important.
They weren’t the first hackers.
They weren’t always ethical.
They certainly weren’t harmless.
But they were among the people who helped turn hacking from a niche technical hobby into a cultural phenomenon—and eventually into one of the foundations of modern cybersecurity.
The BBSs are gone.
The 300-baud modems are museum pieces.
The floppy disks have mostly disappeared.
But the central question remains exactly the same:
What happens when someone becomes curious enough to find out how a system really works?
In cybersecurity, that question can be dangerous.
It can also be incredibly valuable.
And the Legion of Doom understood that long before the rest of the world did.
Sources
- U.S. Secret Service / contemporary reporting on Operation Sundevil — contemporary coverage from The Washington Post and Los Angeles Times.
- Phrack Magazine — original archive of The Conscience of a Hacker by The Mentor.
- Electronic Frontier Foundation — historical material on the Steve Jackson Games raid and Operation Sundevil.
- Bruce Sterling, The Hacker Crackdown — historical account of the Legion of Doom and its Technical Journal.
- Masters of Deception by Michelle Slatalla and Joshua Quittner — detailed history of the LOD/MOD rivalry.
- Legion of Doom historical overview — membership, Technical Journals and organizational history.
Add Tech2Geek as a preferred source on Google to see more of our latest tech articles.
Support Tech2Geek ❤️
Did this guide help you? If Tech2Geek saves you time or helps you solve a problem,
consider buying me a coffee. ☕
Your support helps keep Tech2Geek independent and free.
Comments